AI × SECURITY VIEWERRead the attacker’s intent. Monitor daily → Register fingerprints
From scattered records to a single “intent”.
Research that LMR runs every day on its own network.
01 / CONCEPTAbout this system
Security Viewer Records, made readable.
Devices on the internet receive countless connection attempts from around the world every day. Most are automated scans, and the activity that really needs attention tends to be buried among them. The Security Viewer research gathers the records of network devices and servers in one place, makes them visible, and has AI work out “what is this party trying to do?”
Records gathered
Network device logs, web server access logs, DNS queries and traffic flows, with the records of several sites brought together in one place.
What it shows
Where attacks come from and where they head, event counts over time, the risk of each source, the attack stage with an explanation of intent, and the attack tools whose behaviour is similar.
Daily research
Every day, AI studies newly released attack tools and registers the traces (fingerprints) each would leave in network logs when used.
Visualisation Intent inference Fingerprints
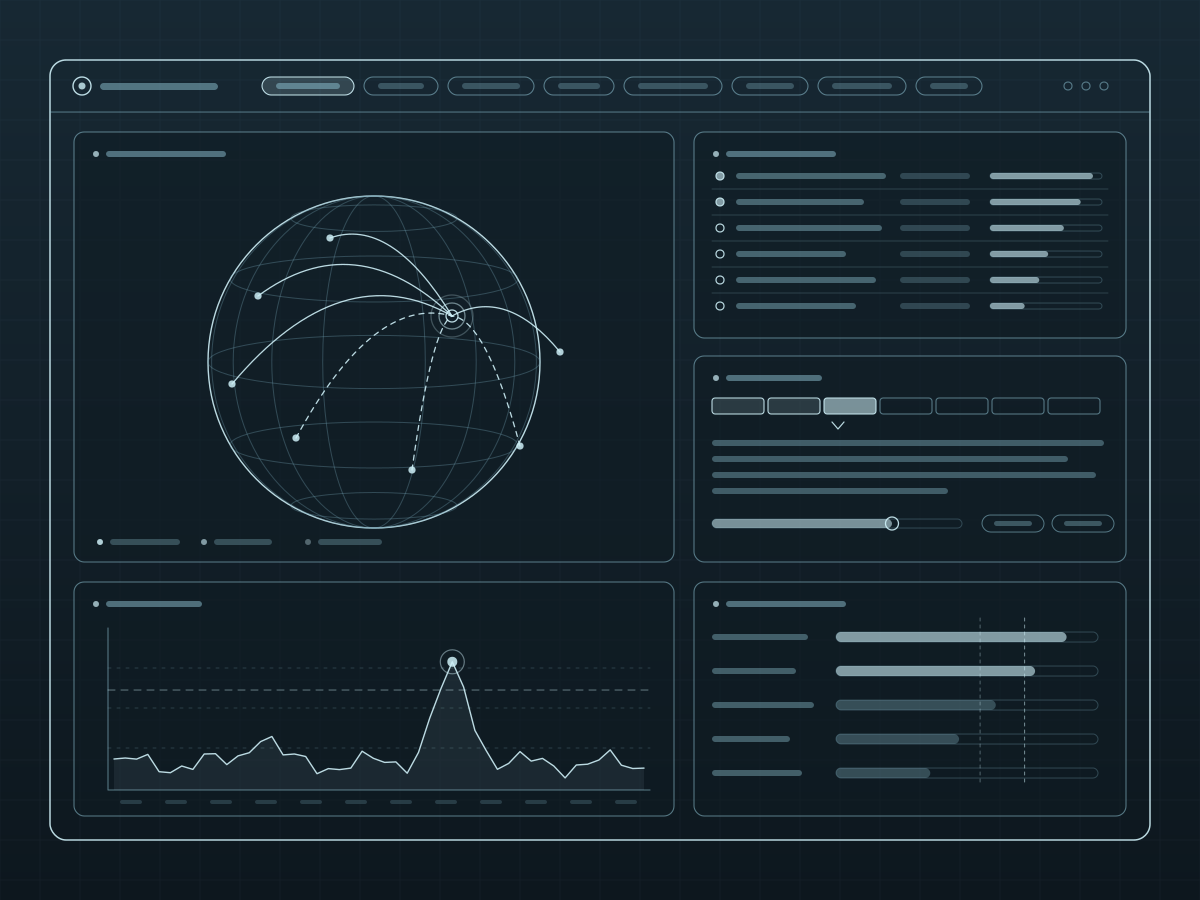
VIEWER SKELETONScreen layout
How the Security Viewer screen is laid out. No real records or addresses appear; only the layout of the screen is drawn in lines.
KEY IDEA
Not only “what happened”, but “what they are trying to do”.
02 / THREE FUNCTIONSSee, read, prepare
Three functions Make it visible, read it, get ahead of it.
See Attack sources and targets on a globe, event counts on a graph. One screen also shows when the same party is hitting several sites.
Read AI reads the records of a source that needs attention in time order and explains the attack stage, the intent and the likely next move in plain sentences.
Prepare Every day, AI studies newly released attack tools and registers their fingerprints, so that even a tool seen for the first time can be caught by its similar behaviour.
03 / READING INTENTWhat the AI reads
Intent inference Reading purpose from a sequence of records.
Each record is only a fragment: where from, where to and when. AI reads the records of a source that needs attention in time order, and infers what the attacker is trying to do from the kinds of destinations targeted, the intervals, how the attempts repeat and how far they spread across sites.
Clues
Intent also shows in timing. A burst in a short time suggests an automated tool; small steps spread over days may be groundwork for a serious attack.
Past cases
AI refers to past verdicts that people have confirmed, which keeps its judgements consistent.
Where the AI runs
The AI that reads network logs runs on our own GPU servers, so records are analysed without being sent to outside AI services.
AI OUTPUTWhat an analysis contains
Item
What it shows
Attack stage
Where it stands: reconnaissance, preparation, delivery, intrusion, installation, remote control or acting on objectives
Attack type
Port scans, password brute force, attacks on web weaknesses, remote-control traffic and more
Intent
A summary of what they are trying to do, with a detailed explanation
Next move
The attacks likely to come next
Correspondence
Recommended responses
Risk
A score from 0 to 100, with the reason
Stage and type come with a confidence level, all in words people can read.
Zero-day readiness Studying new attack tools every day.
New attack tools are released almost every day, and a freshly released tool is rarely covered by existing detection signatures. So every day, AI studies newly released attack tools and registers the traces each would leave in network logs as that tool’s “fingerprint”.
01
Find
Every day, newly released attack tools and penetration-testing tools are found in public information.
02
Study
Its documentation and source code are read to extract how it behaves on the network when used: the kinds of destinations it targets, its intervals, its order and its spread. The tool’s code is never run.
03
Register
The traits become numbers on more than 20 dimensions, registered as the tool’s fingerprint.
04
Match
We measure how close a real source’s behaviour comes to each fingerprint. Even without an exact match, behaviour that comes close is recognised as “similar to this tool”.
What is registered
Fingerprints of more than 100 tools (as of November 2026)
From long-established port scanners and bots that target IoT devices to new remote-control (C2) tools
Vulnerability checks, brute-force logins, and probes aimed at cloud and AI systems
The daily research has run since June 2026
Fingerprints that AI has newly registered are treated as “weak evidence” until they are confirmed, and never produce a strong verdict on their own. This keeps false alarms down.
KEY IDEA
Catch the tool by its habits, not the attack by its pattern.
05 / HOW IT WORKSGather, measure, interpret
Five stages From records to words people understand.
01Gather
Records from network devices at several sites, web servers, DNS and traffic flows are gathered and stored in one place.
02Score
Each source gets a risk score from the number of destinations it tried, how often it was refused, how far it spread across sites and more.
03Match
Each source’s behaviour is compared with the registered fingerprints to show which tools it resembles.
04Interpret
AI reads the records of high-scoring sources and explains the attack stage, the intent and the next move.
05Notify
Results appear on screen, and important ones go to the people in charge at once. Verdicts that people confirm feed the next analysis.
06 / DESIGN PRINCIPLESWhat matters in the design
Four principles A tool built to protect must not become a new weakness.
PRINCIPLE 01
AI explains
AI reads the records and states the intent and its grounds in words. The verdict itself rests on tested rules and scores, and is kept in a form people can check.
PRINCIPLE 02
Logs are read in-house
The AI that reads network logs runs on our own GPU servers. The daily research reads public information only.
PRINCIPLE 03
Keep false alarms down
New fingerprints are treated as weak evidence until confirmed and never produce a strong verdict on their own. What people confirm feeds into the next verdicts.
PRINCIPLE 04
Trust nothing we study
We never run attack-tool code. Public text can hide instructions meant to trick an AI, so everything we study is treated as untrusted.
07 / STATUSWhere we are now
Where the research stands Running every day on our own network.
We run the Security Viewer every day on the network that links LMR’s sites while the research continues. We test it against records of real attacks and feed each problem we find into the next improvement.
Working now
Visualising records, scoring the risk of each source, inferring intent with AI and matching tool fingerprints. The study of new attack tools and the registration of their fingerprints run automatically every day.
In progress
Widening what we can see (more kinds of records) and making the AI’s explanations and the fingerprint matching more reliable.
Technologies
Log search and visualisation, feature vectors and similarity matching, a large language model (on our own GPU servers) and retrieval of past cases (RAG).
NOTE
The screen drawing shows the layout only and contains no real records or addresses.
Attack tools are studied from public information only, to learn the traits we use for defence.
We do not promise that every attack will be detected.